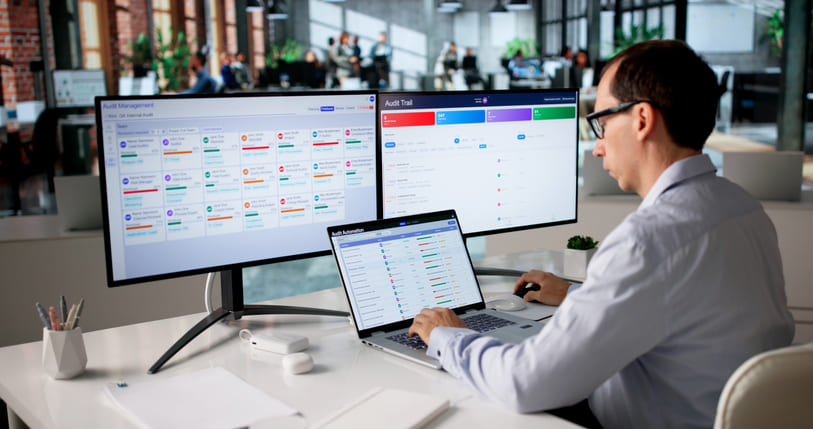
When a customer, auditor or regulator asks who decided what, your software should answer in minutes, so build the audit trail before launch.
Sooner or later, every business system is asked a question it was never designed to answer: who changed this, when, and on what basis? Niral Dhameliya, Partner and CTO of Empiric Infotech LLP, works on business platforms where that question is part of the brief, including a procurement platform in Germany that runs IT maintenance tendering as online auctions. His advice is direct: decide what your audit trail must prove before the first release. Logging added after launch is partial, costly and hard to trust.
Who Asks “What Happened?” and What Do They Need?
Most companies treat audit trails as an IT concern. In practice, the people who ask for them sit elsewhere in the business, and they usually ask under pressure.
A customer disputes an invoice or a decision. A manager wants to know why a record changed overnight. An auditor asks who approved a payment or a contract. A data protection authority asks how personal data was handled. Under the GDPR’s accountability principle, a company must not only comply but be able to demonstrate that it complies, and a reliable record of what happened is a large part of that proof.
Each of these people needs the same five answers:
Who acted: a named user, a role or an automated process.
What changed: the state before and the state after.
When it happened, recorded in one consistent time zone.
Under which rule: the policy, setting or version that applied at that moment.
On whose authority: who approved it, if approval was required.
If a system can answer those five questions for the decisions that matter, it can explain itself. If it cannot, someone will rebuild events from emails and memory, and the result will satisfy no one.
Which Events Deserve a Record?
Not every click needs logging. The events that matter are the ones that change money, rights or obligations.
On the procurement platform, IT system owners publish maintenance tenders as auctions, maintenance providers submit ranked bids, and administrators oversee both sides. Each auction moves through guarded states: draft, active, closed and awarded. Those transitions, the bids, the supplier scores and the contracts generated from an award are exactly the moments a losing bidder or an auditor may question later. The goal was a fully auditable auction process with fair, defensible supplier selection, so these events were designed into the workflow itself.
A useful test for any system: if a decision could be disputed, appealed or audited, record it. That usually covers:
Status changes on core records such as orders, applications, tenders and contracts
Approvals, rejections and overrides
Changes to prices, scores, limits or permissions
Data exports and bulk changes
The version of any rule or scoring model used to make a decision
That last point is often missed. The procurement platform scores providers with a configurable evaluation model, and a configurable model is only defensible if the trail shows which configuration produced each score. A score with no record of the rules behind it invites challenge.
What Should You Leave Out of the Log?
An audit trail can become a privacy problem of its own. Logs are copied, backed up and shared with support teams, and they are often kept longer than the data they describe. The GDPR principle of data minimisation applies to logs as much as to any other store of personal data.
The OWASP Logging Cheat Sheet gives a practical list of what to exclude, and the same thinking works for business audit trails:
Record
Leave out or mask
Why
User ID and role
Passwords, access tokens, session IDs
Credentials in logs are a security risk
Record ID and the fields that changed
Full copies of personal records
Point to the record instead of copying it
Before and after values of business fields
Bank details, health data and other sensitive fields
Mask them, or record only that they changed
The rule or version applied
Free-text notes that may contain personal data
Structured reasons are easier to search and safer
Timestamp and source
Entries older than the agreed retention period
The log needs its own retention rule
The aim is a trail that proves what happened without becoming a second, less protected copy of the customer database.
Why Does Logging Added After Launch Cost More?
Teams often plan to add audit logging later. It rarely goes to plan, for three reasons.
First, history cannot be backfilled. Every event before the logging goes live is lost, and the first serious dispute often concerns exactly that period.
Second, retrofitting touches everything. Late logging has to be inserted wherever data changes: screens, imports, background jobs and integrations. Some places get missed, and a trail with gaps is hard to rely on.
Third, late logs are easy to doubt. If the administrators who can change records can also edit or delete the log, the trail proves little. Designing for this from the start means append-only storage, restricted access and, where the stakes justify it, tamper-evident records. The NIST guide to computer security log management treats log integrity and retention as planning decisions, made before systems go live.
When state changes are designed as controlled steps, as the auction lifecycle was, each step can write its own record at the moment it happens. The log becomes a by-product of the workflow instead of a separate system attached afterwards.
Built in from the first release
Added after launch
History
Complete from day one
Starts on the day logging went live
Coverage
Every change passes through the same controlled steps
Depends on finding every place data changes
Trust
Append-only and access-controlled by design
Often editable by the people it should check
Effort
Part of normal feature work
A separate project that touches every feature
How Can Managers Use the Trail, Not Only the IT Team?
An audit trail that only a developer can read will not be used when it matters. Three design choices make it useful to the business:
Plain event names. “Auction closed by scheduler” is more useful than a database code. If the software runs in more than one language, as the procurement platform did in English and German, event names need translating like any other part of the interface.
A timeline for each record. Managers think in terms of one contract, one customer or one tender. Let them open a record and see its full history in order.
Filters and export. Auditors ask for “all changes by this user in March” or “every award above a set value”. A filtered export saves days of manual work.
Which Three Questions Should You Ask Before the Build Starts?
Whether software is built in-house or with an outside team, these questions belong on the table before development begins:
Which decisions in this system could be disputed, and by whom? The answer defines what must be recorded.
How long must we keep the evidence, and how do we keep personal data out of it? The answer defines retention and masking.
Who can change or delete a log entry, and how would we know? The answer defines whether the trail can be trusted.
Conclusion
Audit trails are cheapest and most trustworthy when they are designed together with the workflow they describe. The procurement platform shows the pattern: guarded steps, a record of each decision and the rules behind it, and logs that respect data protection. Looking ahead, the question “who decided?” will more often have an automated answer, as rules engines and AI tools take actions inside business software. Systems that record which process acted, and under which configuration, will be far easier to defend.
Acknowledgements
The author used AI-assisted writing tools to help draft and edit this article. The examples come from his company’s project work, and he reviewed and approved the final text.
Niral Dhameliyais a Partner and the CTO of Empiric Infotech LLP, a custom software development company with offices in Surat, India and Bridgeville, Pennsylvania. He oversees business platforms built with Flutter, React, Node.js and Python, with a focus on software architecture, data protection and remote engineering teams.
The European Business Review uses cookies to improve site functionality, provide you with a better browsing experience, and to enable our partners to advertise to you. Detailed information on the use of cookies on this Site, and how you can decline them, is provided in our Privacy Policy and Terms and Conditions. By clicking on the accept button and using this Site, you consent to our Privacy Policy and Terms and Conditions. ACCEPT Reject
Privacy & Cookies Policy
Privacy Overview
This website uses cookies to improve your experience while you navigate through the website. Out of these cookies, the cookies that are categorized as necessary are stored on your browser as they are essential for the working of basic functionalities of the website. We also use third-party cookies that help us analyze and understand how you use this website. These cookies will be stored in your browser only with your consent. You also have the option to opt-out of these cookies. But opting out of some of these cookies may have an effect on your browsing experience.
Necessary cookies are absolutely essential for the website to function properly. This category only includes cookies that ensures basic functionalities and security features of the website. These cookies do not store any personal information.
Any cookies that may not be particularly necessary for the website to function and is used specifically to collect user personal data via analytics, ads, other embedded contents are termed as non-necessary cookies. It is mandatory to procure user consent prior to running these cookies on your website.